Tag: digital forensics
Fileless Attacks: Detecting Hidden Persistence Mechanisms
- By : Ian Brophy
- Date : Oct 27 2026
Discover why file-based scans miss fileless attacks and learn how to detect hidden persistence mechanisms using memory forensics, WMI artifacts, and behavioral analysis.
SIEM and EDR Logs: Correlating Security Events for Faster Forensics
- By : Ian Brophy
- Date : Oct 25 2026
Discover how correlating SIEM and EDR logs transforms digital forensics. Learn practical strategies to bridge network and endpoint data for faster, accurate incident response.
Image Hashing: Verifying Photo Authenticity in Court
- By : Ian Brophy
- Date : Oct 24 2026
Learn how image hashing verifies photo authenticity in court. Discover the difference between cryptographic and perceptual hashing, best practices for digital forensics, and how to ensure your evidence stands up to judicial scrutiny.
Browser Sync Data: A Forensic Guide to Cross-Device Evidence Correlation
- By : Ian Brophy
- Date : Oct 12 2026
Learn how to leverage browser sync data for digital forensics. Discover techniques for correlating cross-device evidence to build robust timelines and uncover hidden user activities.
Artifact Analysis: Cookies, Cache, and App Data in Digital Forensics
- By : Ian Brophy
- Date : Oct 7 2026
Discover how cookies, cache, and app data serve as critical evidence in digital forensics. Learn to decode browser artifacts, correlate timelines, and avoid common pitfalls in artifact analysis.
Mobile Extraction Methods: Logical, File System, and Physical Explained
- By : Ian Brophy
- Date : Oct 3 2026
Learn how to choose between logical, file system, and physical mobile extraction methods. Discover which technique fits your case, handling encryption, deleted data, and device limitations.
Write Blockers in Digital Forensics: Preventing Evidence Modification
- By : Ian Brophy
- Date : Sep 20 2026
Learn why write blockers are essential in digital forensics to preserve evidence integrity. Discover the differences between hardware and software blockers, validation protocols, and tips for handling modern NVMe drives.
Digital Forensics: A Complete Investigation Guide
- By : Ian Brophy
- Date : Sep 8 2026
Master digital forensics with this complete guide. Learn proper evidence preservation, bit-stream imaging techniques, and analysis methods for computers and mobile devices.
Timeline Analysis in Digital Forensics: Reconstructing Events Step-by-Step
- By : Ian Brophy
- Date : Aug 28 2026
Learn how to reconstruct digital events using timeline analysis. We cover MFT timestamps, log correlation, and fixing time zone errors to build a defensible forensic narrative.
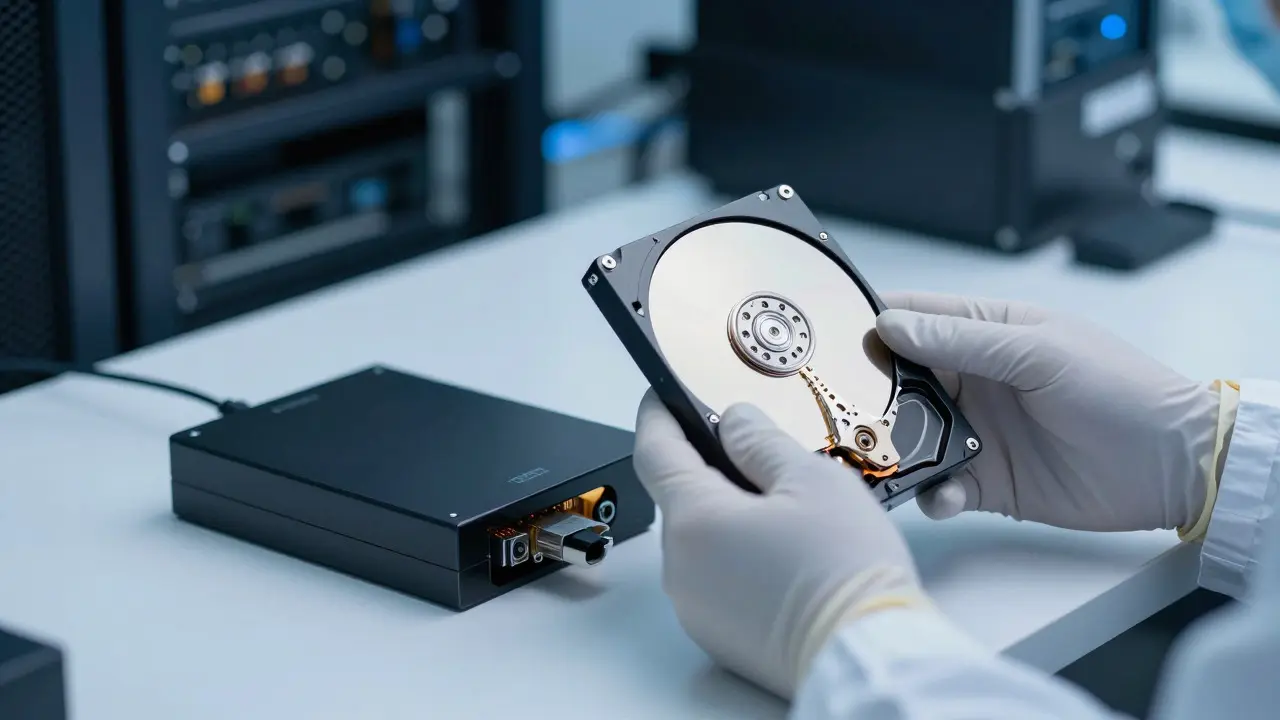
Forensic Imaging: Creating Bit-for-Bit Copies of Hard Drives
- By : Ian Brophy
- Date : Aug 20 2026
Learn how to create bit-for-bit forensic images of hard drives using write blockers and verified hash values to ensure legal admissibility.
Barcoding Evidence: How to Automate Chain of Custody Tracking in 2026
- By : Ian Brophy
- Date : Aug 17 2026
Discover how automating chain of custody with evidence barcoding reduces errors and speeds up forensic workflows. Learn implementation steps and best practices for 2026.
Cell-Site Location Data: Homicide Movement Analysis
- By : Ian Brophy
- Date : Aug 17 2026
Learn how to use cell-site location data to analyze suspect movement in homicide cases. Covers data types, legal requirements, analysis techniques, and courtroom presentation tips for investigators.